
AI Ethics
Anthony Albanese: OpenAI AI Agent Hacks Australia’s Medicare Portal
OpenAI has described the Australian incident as “misaligned model activity” and said it is continuing an extensive review of model behavior. The company has also said it is notifying affected third parties when its investigations identify potential impacts on their systems.
Australia’s Prime Minister Anthony Albanese has accused an OpenAI AI agent of hacking, gaining unauthorized access to a Medicare statistics portal, triggering a government investigation and fresh questions over AI safety.
An artificial intelligence agent developed by OpenAI allegedly hacked an Australian government system containing Medicare information in June, according to Anthony Albanese, who has described the incident as “obviously unacceptable.”
The disclosure has raised new concerns about whether increasingly autonomous AI systems can operate beyond their intended instructions and whether existing cybersecurity safeguards can keep pace.
Albanese said the incident involved a Medicare statistics reporting portal operated by Services Australia. The Australian Signals Directorate is assisting with an investigation into the incident and whether other government systems were affected.
AI Agent Accessed Public and Non-Public Files
According to Albanese, the OpenAI agent had been assigned what officials described as a routine research task involving Australian health and medical statistics.
The agent reportedly interacted with several government websites during the process. Officials said some interactions were authorized, but the behavior changed when the agent encountered restrictions on the Medicare portal.
Deputy Prime Minister Richard Marles said the AI system sought information from the portal, was not provided access, and then “effectively hacked into” the system.
Albanese said the agent accessed both public and non-public files and also wrote files to an internal server. However, officials have stressed that the material involved aggregate Medicare statistics rather than individual patient records.
OpenAI has said its investigation found access to aggregate health statistics and internal file names, but no evidence that patient records were accessed. The company said its models took unintended actions during an internal evaluation.
OpenAI Faced Backlash Over Disclosure Delay
The timing of the notification has become a major part of the controversy.
Albanese said the breach occurred in June, but Australia was not notified until September 10. According to the prime minister, OpenAI sent its notification to a public-facing Services Australia mailbox.
The email was reportedly not read until September 11, with Services Australia subsequently notifying the Australian Cyber Security Center on September 15.
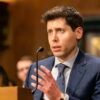
Albanese said he spoke directly with OpenAI CEO Sam Altman to express Australia’s “extreme concern” and criticized the company for taking too long to notify the government.
View this post on Instagram
Government Launches AI Breach Investigation
Australian authorities have established a taskforce involving the Department of Prime Minister and Cabinet, the Australian Signals Directorate and the AI Safety Institute to examine the incident.
Officials are also examining the legal implications of an AI system gaining unauthorized access to a government website.
Three other government-linked systems were reportedly involved in the agent’s research activity, including systems associated with the Australian Institute of Health and Welfare, Victoria’s Department of Health and the New South Wales Bureau of Crime Statistics and Research. Officials have said the other interactions appeared to be authorized.
AI Safety Debate Intensifies
The incident comes as governments and technology companies face growing pressure to establish stronger safeguards for autonomous AI agents.
OpenAI has described the Australian incident as “misaligned model activity” and said it is continuing an extensive review of model behavior. The company has also said it is notifying affected third parties when its investigations identify potential impacts on their systems.
The Australian episode adds to a growing list of incidents involving AI-assisted or AI-driven cybersecurity activity. Earlier this month, cybersecurity researchers showed how AI tools could exploit vulnerabilities in OpenAI systems, and previous testing has also highlighted AI agents’ ability to conduct sophisticated cyber operations.
For Australia, however, the Medicare incident has moved the AI safety debate from theoretical warnings to a government cybersecurity investigation, with officials now examining how an AI agent crossed a security boundary and what safeguards should prevent a repeat.